Use Pin with Microsoft 365
The easiest way to enable Pin with Microsoft 365 is for an admin to log into Pin and grant consent on behalf of your organization.
Accept consent during login
A Microsoft 365 admin needs to log into Pin using our consent link: https://api.pin.com/auth/microsoft/consent
The admin will need to check "Consent on behalf of your organization" so that other users can authenticate with Pin.
Allow access through Microsoft Entra ID
(Previously "Microsoft Azure Active Directory" — Microsoft renamed this service in 2023. If your organization's admin portal still shows "Azure Active Directory," you're in the same place; it's the same underlying service under its new name.)
Go to the Microsoft Entra admin center to grant consent, or create a policy that allows the application. You'll need to be signed in as at least a Cloud Application Administrator, Application Administrator, or Global Administrator — other roles won't be able to complete this step.
Then follow the steps below:
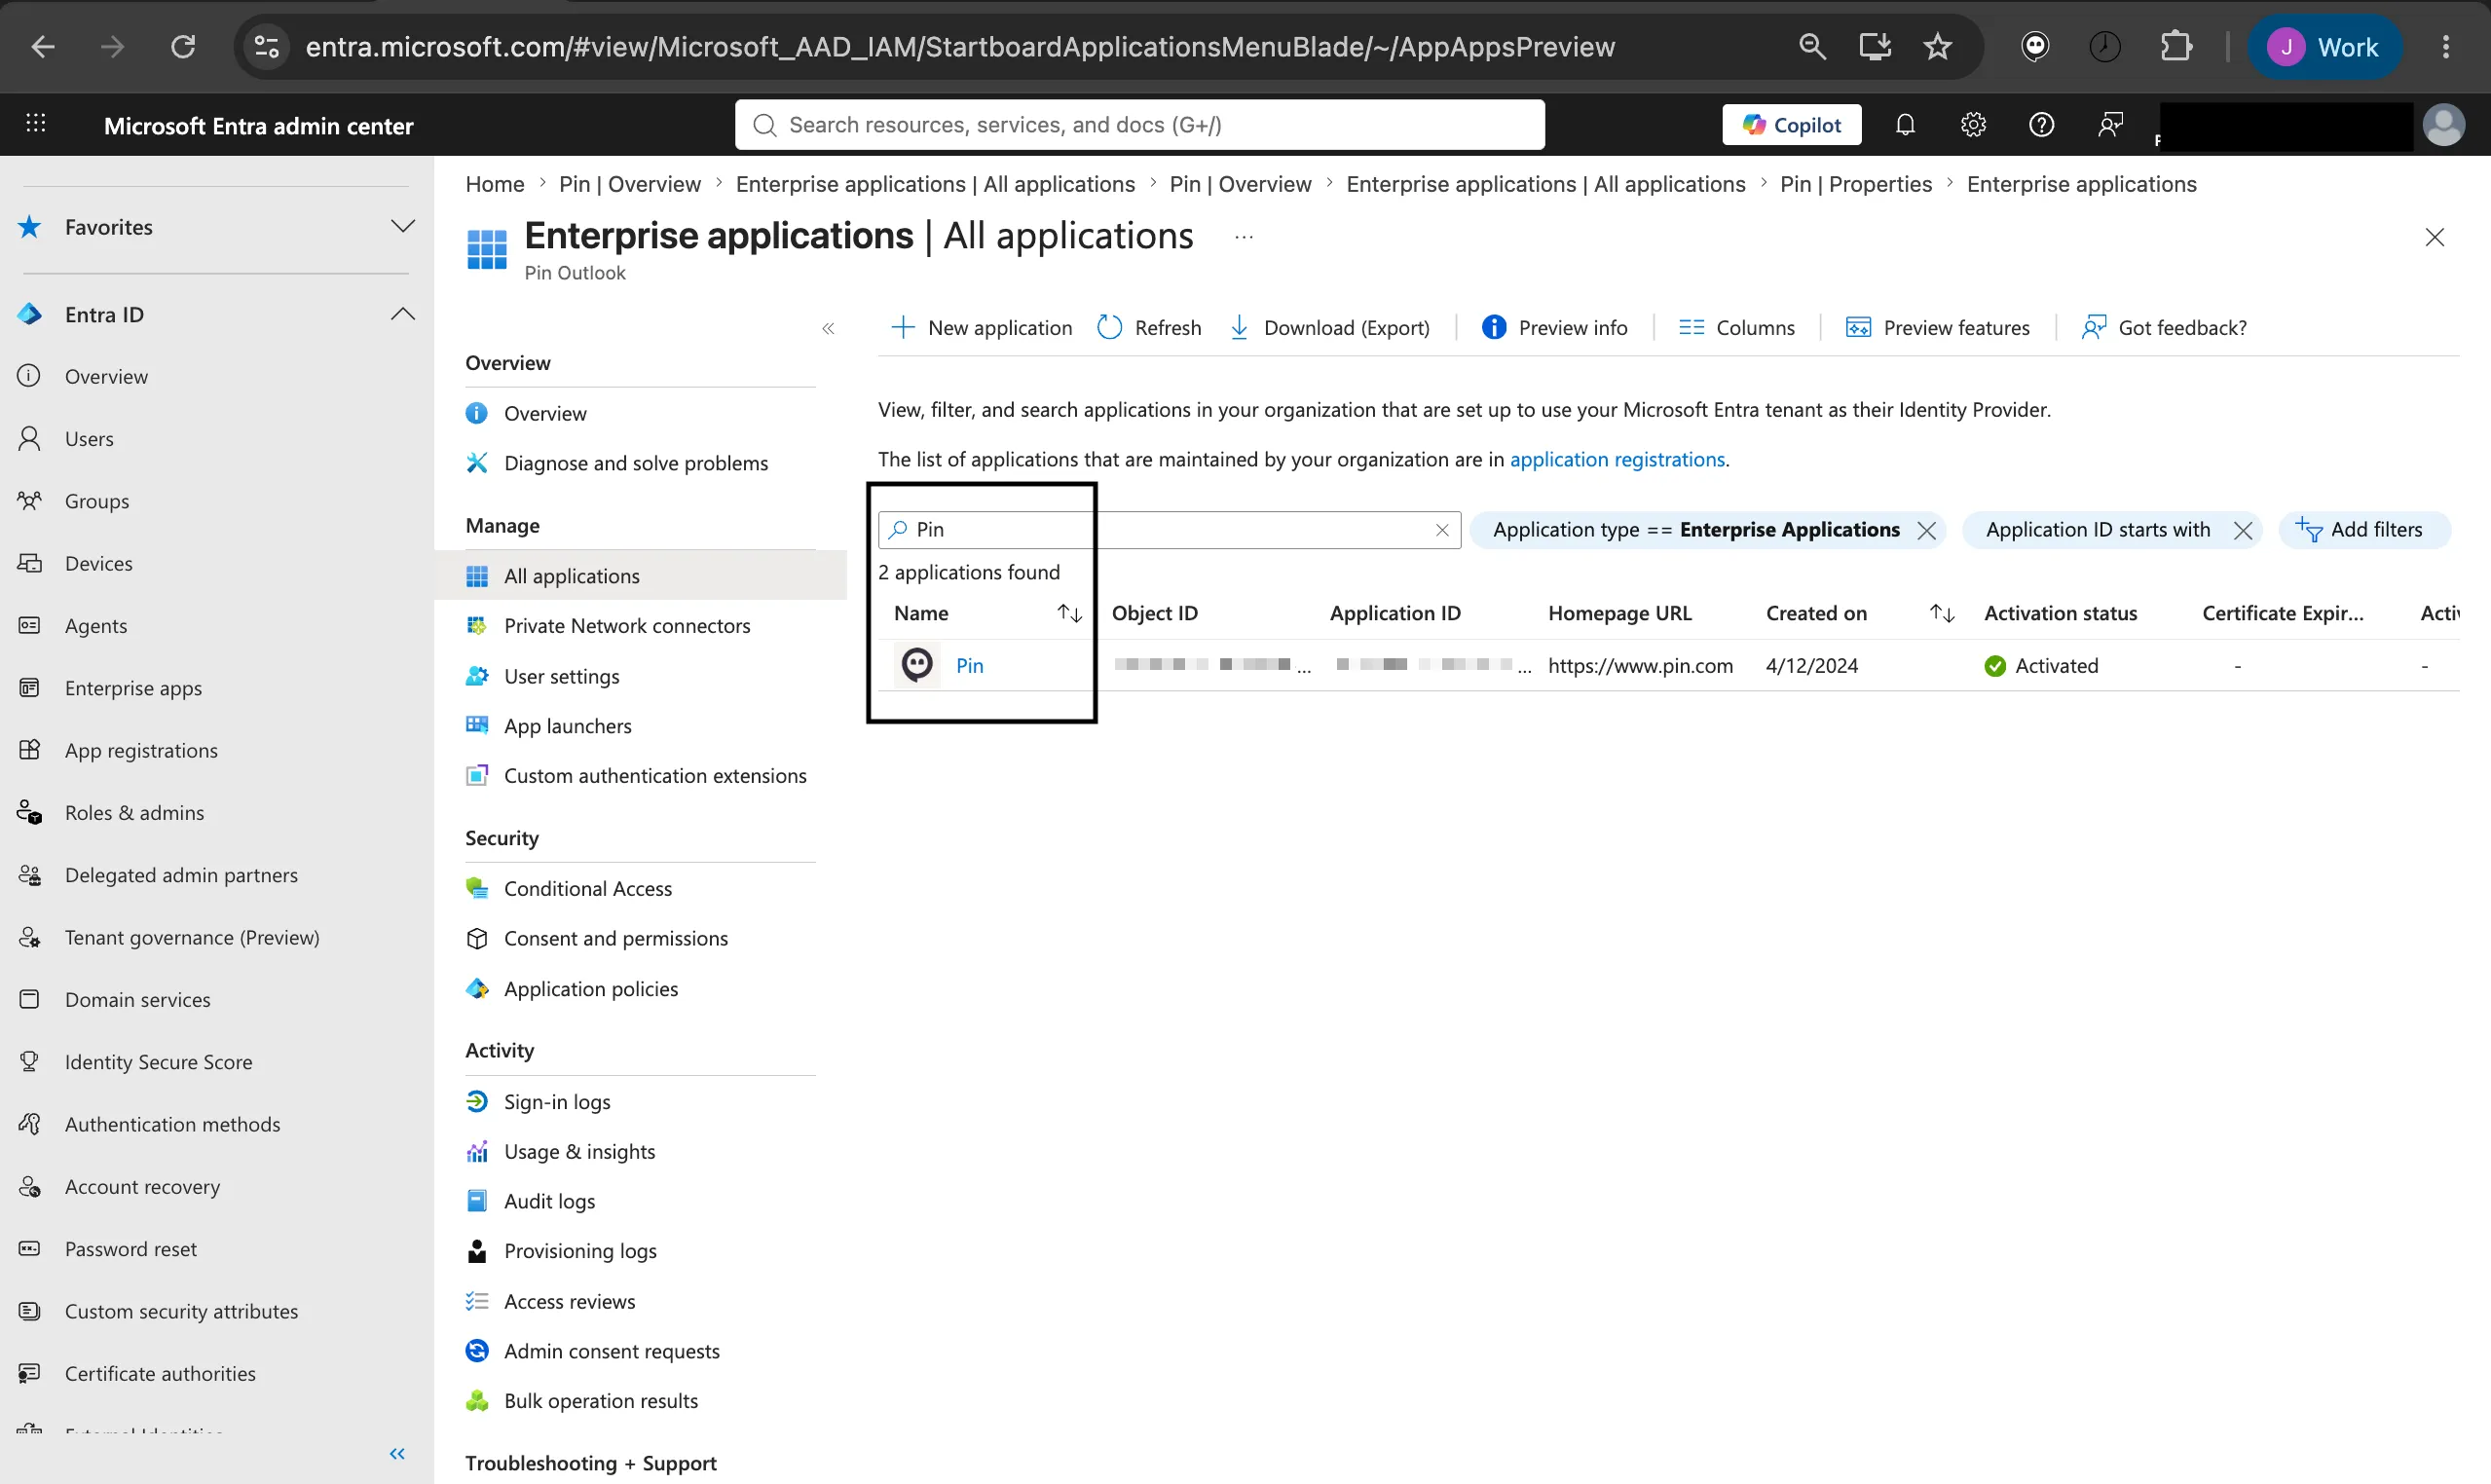
- In the Microsoft Entra admin center, go to Enterprise applications->All applications.
- Search for "Pin" in the list of applications. If Pin doesn't appear in this list: the app is only provisioned in your tenant after at least one user has completed the consent link (https://api.pin.com/auth/microsoft/consent). If it's missing, have a user complete that step first, then check again.
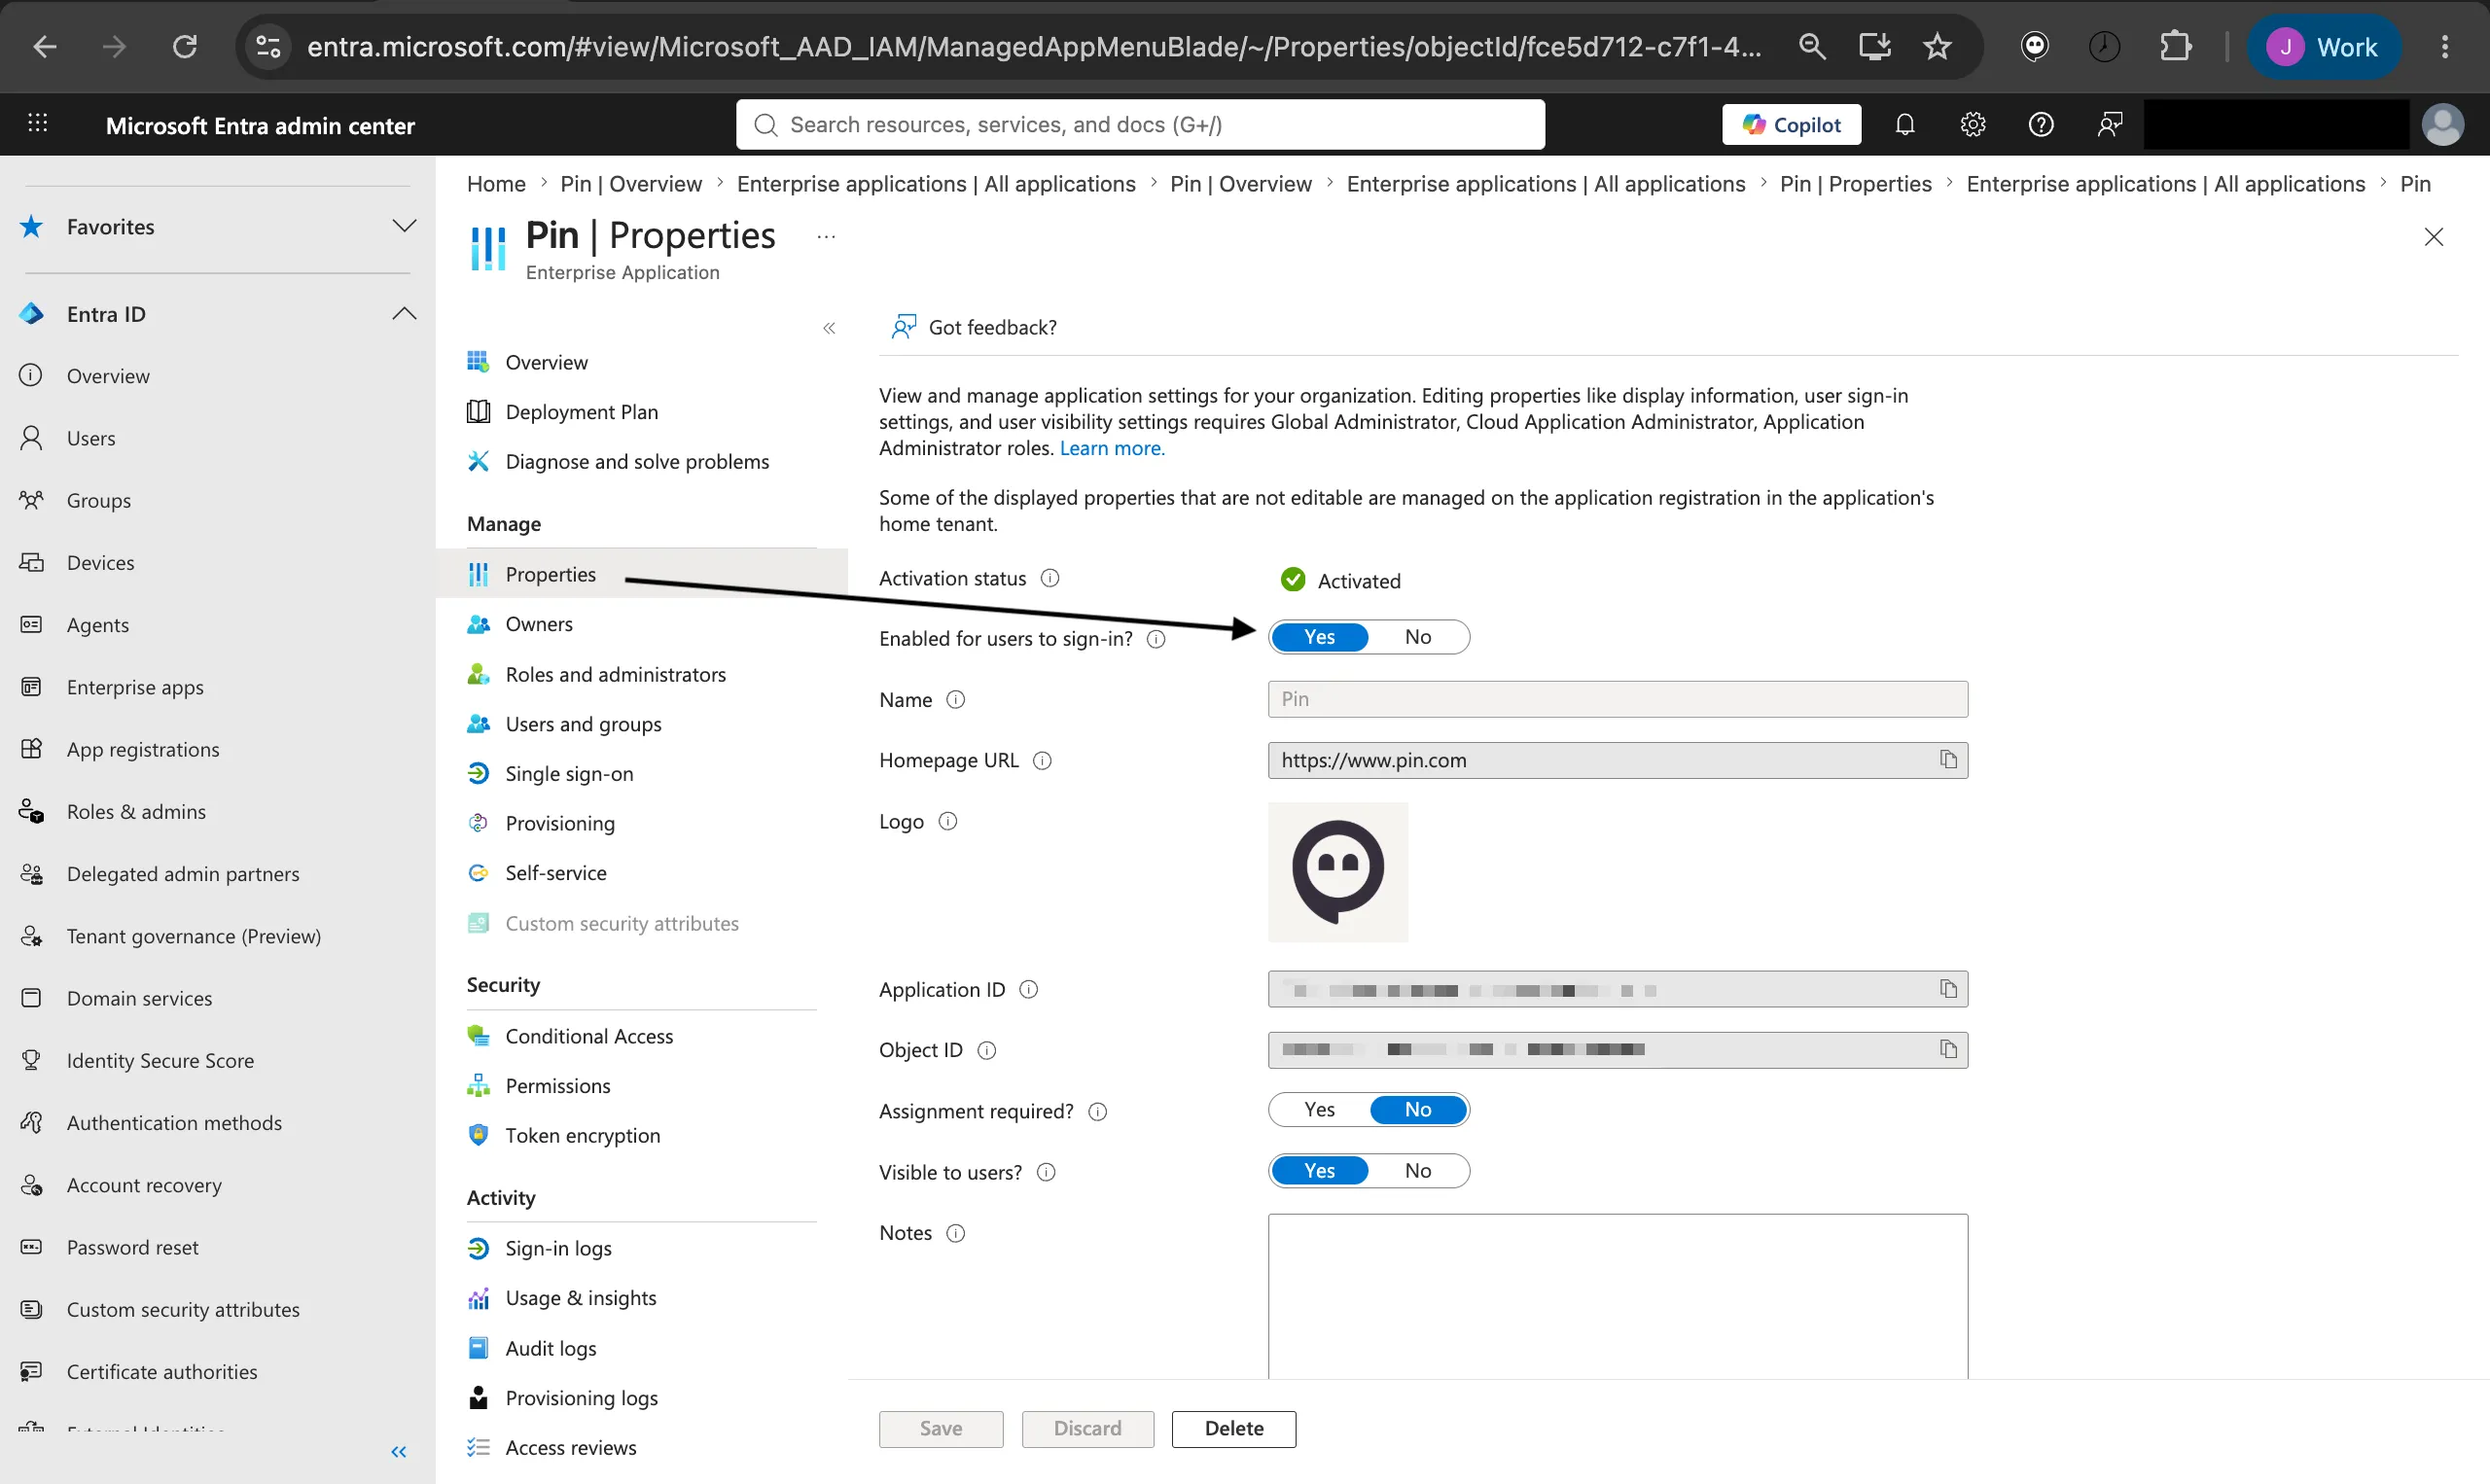
- Open the application, select Properties, and switch "Enabled for users to sign in?" to Yes. This enables Pin and allows your users to authenticate.
- Next, go to Security > Permissions on that same application page.
- Review the listed permissions, then click Grant admin consent for [your organization]. Confirm in the Microsoft consent popup that appears.
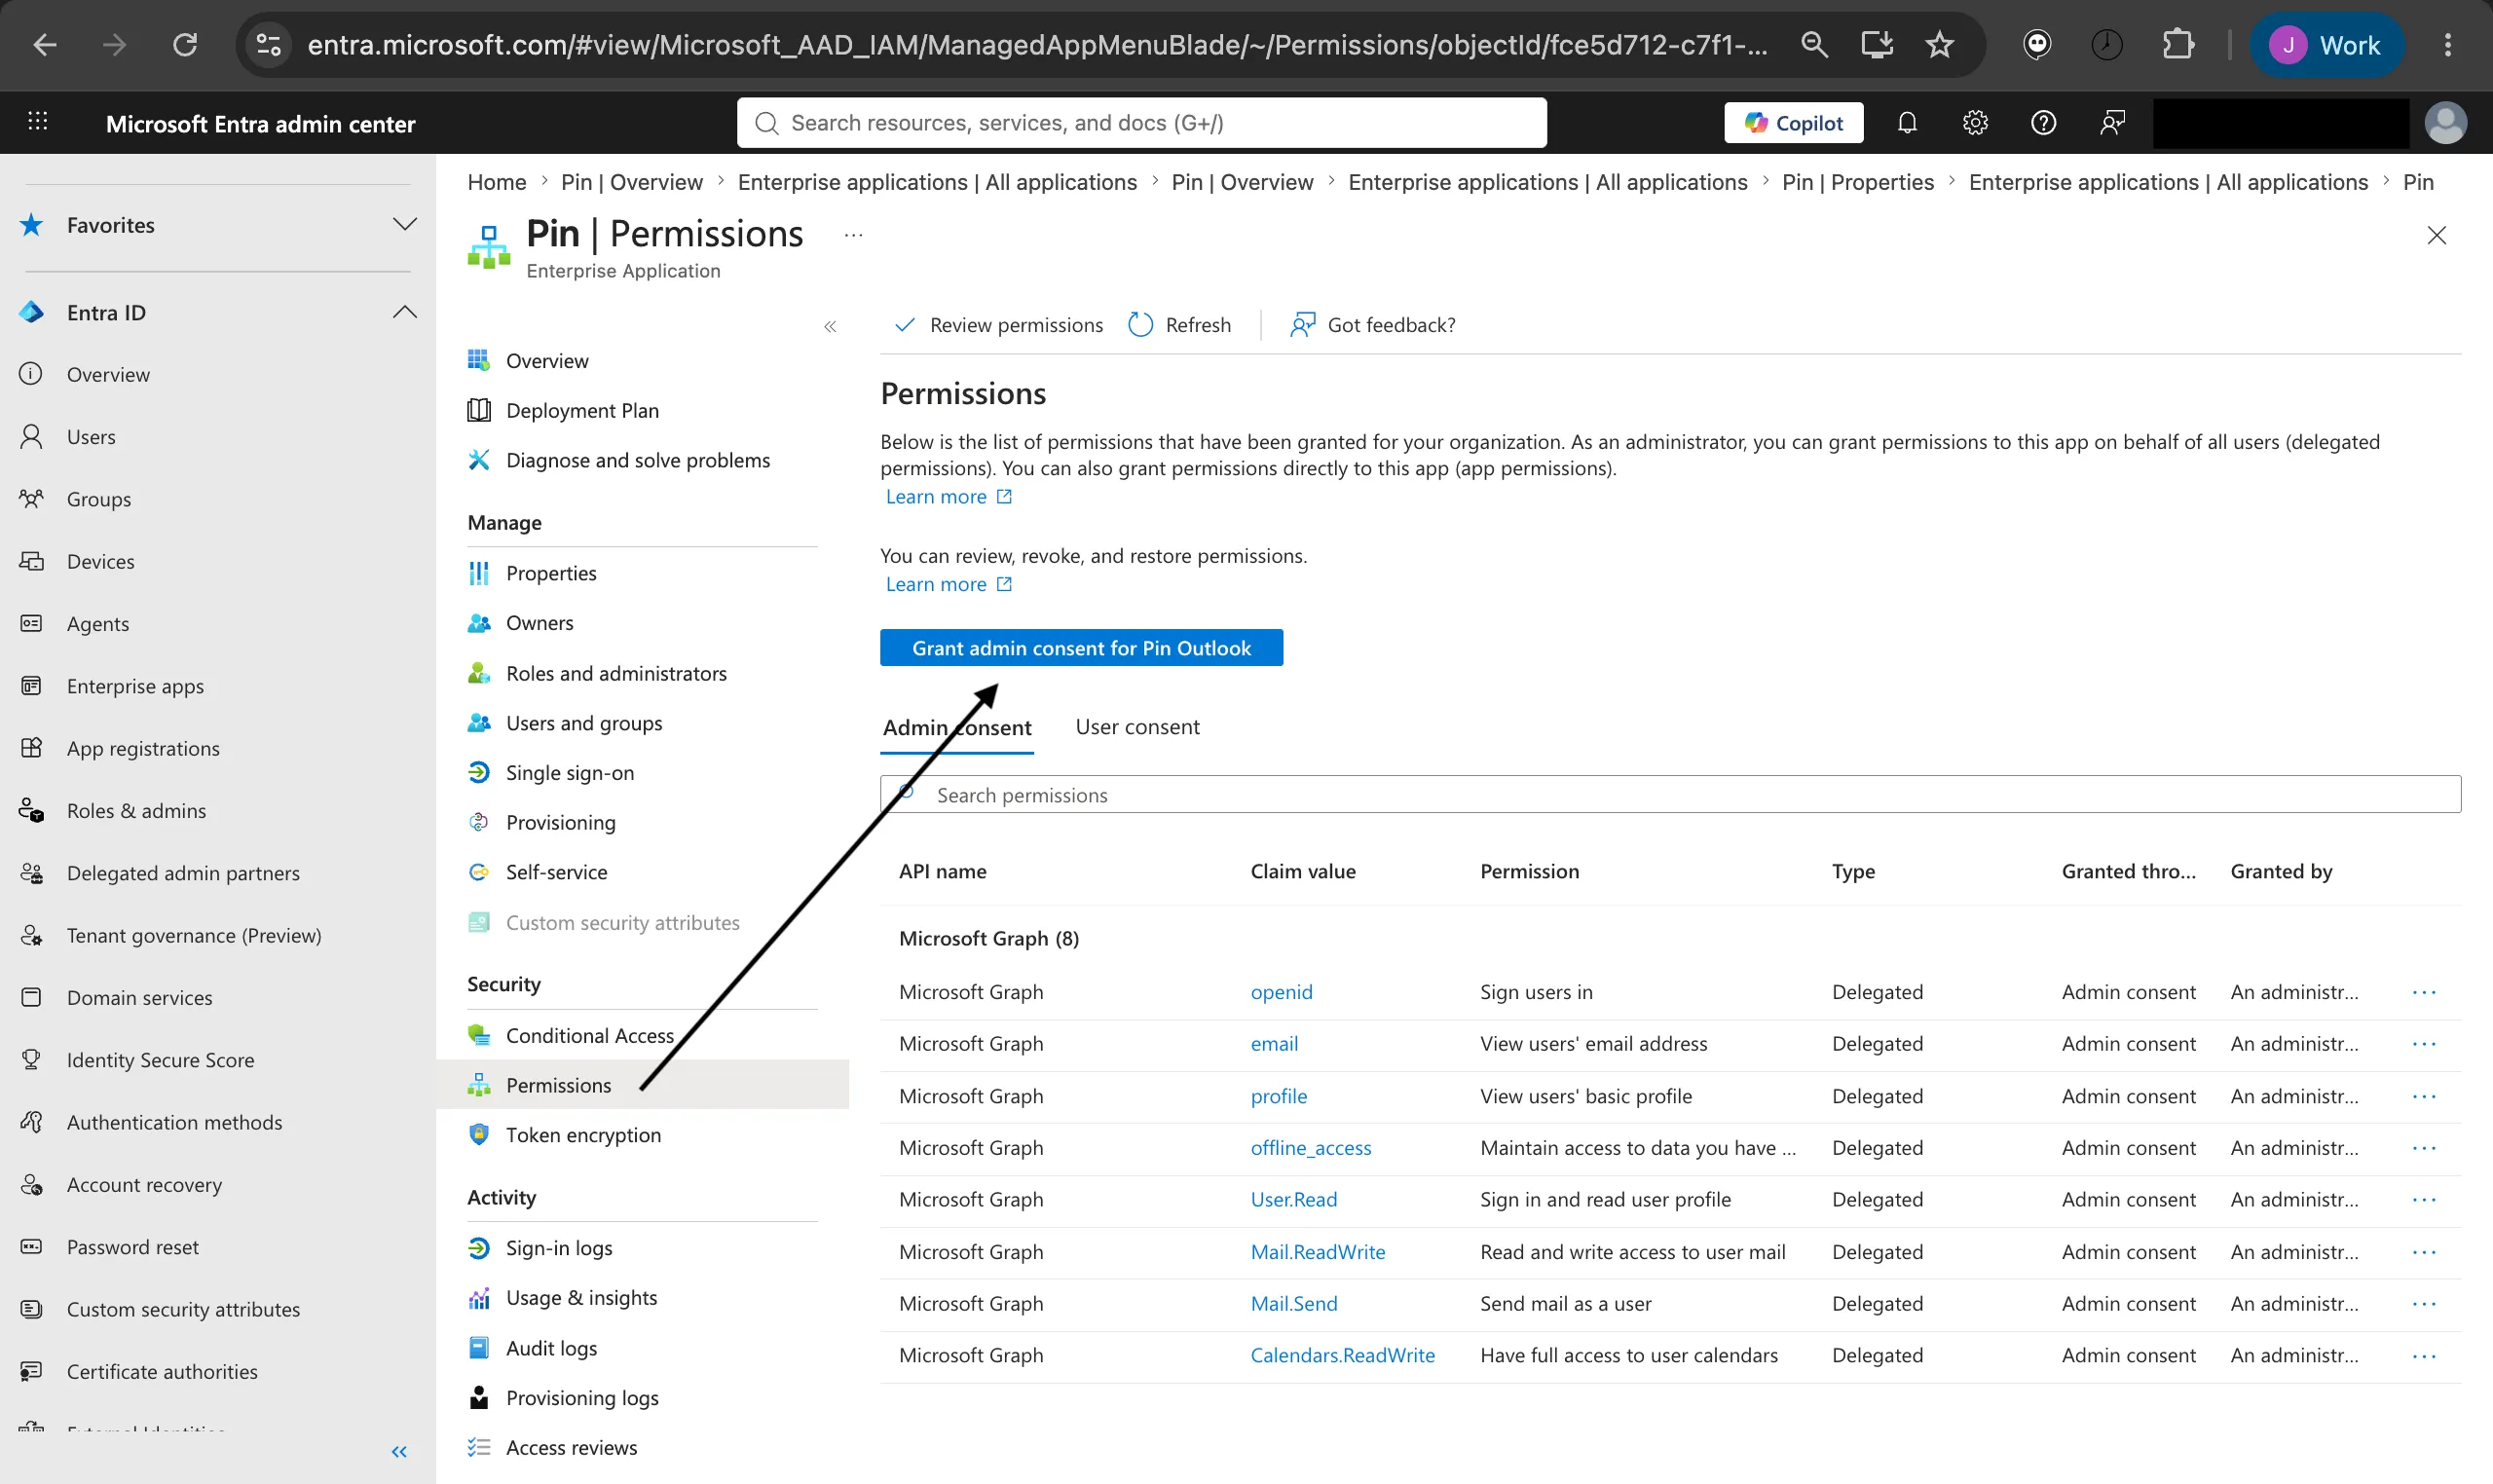
Verify it worked: Back on the Permissions page, you should now see the granted permissions listed with consent type AllPrincipals — this confirms consent was granted tenant-wide, not just for a single user.
Shortcut — pending requests: If your organization has the admin consent workflow enabled, a request may already be waiting for approval. Go to Enterprise applications > Activity > Admin consent requests > My Pending to approve it directly without the manual steps above.
Frequently Asked Questions
If you're looking for why we need these permissions, please review the below:
Permission | Purpose |
|---|---|
openid | Authenticates and signs the user in. |
Reads the user's email address for identification | |
profile | Reads basic profile information, such as name |
offline_access | Allows the connection to remain active and refresh tokens without repeated sign-in. |
User.Read | Reads the signed-in user's Microsoft profile |
Mail.ReadWrite | Reads, synchronizes, and manages mailbox messages. It does not permit sending by itself |
Mail.Send | Sends email as the connected user|mailbox |
Calenders.ReadWrite | Synchronizes and manages calendar events. Pylon uses calendar data to backfill meetings and populate fields such as Last Meeting Date and Next Meeting Date |